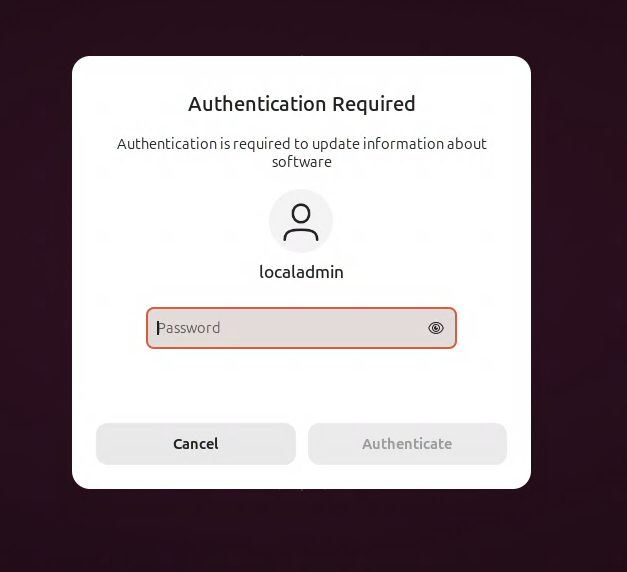
The ubuntu desktop is joined to a windows domain for domain logins and network drive access. It is headless and accessed via RDP. The RDP client is configured under settings → system → remote login. The domain users with access have sudo rights and can sudo in the terminal. All of this is working.
However after logging in the user is prompted by Gnome for the password of the local user created during setup not the currently logged in user. I’m not sure what this prompt is securing. This is also true when accessing settings or trying to shut the machine down or reboot. It will always prompt for the local user rather then the currently logged in domain users password. If the user does enter the local user password it still fails anyway with a message saying sorry that didn’t work. Whats going on here and how can it be adjusted to prompt for the domain users password. At least so they can shutdown / reboot.
Its for the software updates reading helps . Anyway it seems gnomes sudo prompt is always promting localadmin rather then the logged in user that has sudo privileges. Stopping the prompts and being able to shut down the system would be enough. Software updates can be done from the terminal when needed.
Sorry for being brief, do not waste time on xrdp or SSSD
The issue is that GNOME Remote Desktop runs as a non-seat session (no seat0), so logind and PackageKit require admin auth for reboot and updates. And because Polkit checks the local sudo group instead of /etc/sudoers, it only knows localadmin.
Look into adding a custom rule in /etc/polkit-1/rules.d/ and adding your domain users to the local sudo group.
Because those prompts come from the polkit and polkit has nothing to do with sudo. The default polkit rules shipped by Ubuntu check for the active local session. You would need to adapt them to your environment. See as example /usr/share/polkit-1/rules.d/com.ubuntu.desktop.rules for inspiration. All available actions can be listed with pkaction --verbose.
That’s a rabbit hole i’m not going to expend any more time on considering how much effort it was just to get to this point.
Is there another flavour of ubuntu or a linux distribution that would work better as a headless domain integrated pc? Or maybe an alternative way of configuring remote access.
No worries if not I can just slap windows back on it and it’ll do what i need to just fine.
Thanks that seems to have worked, thankyou very much for going out of your way to do that it’s appreciated
I’ve been using ubuntu on my personal desktop and on dev vm’s and servers for years and will definatly continue to do so. This was my first attempt at getting it running as a domain connected desktop pc. Its been an interesting experiment but the amount of effort involved and the results of that effort mean at this moment I wouldn’t do it again. I was hoping i could give some users a domain connected ubuntu laptop. However at this juncture a windows machine running an ubuntu vm is still the simplest option in that scenario. Thanks for all your help.
As a quick tip for the future: if you ever decide to try domain-connected Ubuntu laptops again, take a look at “ADsys” -part of Ubuntu Pro, free for personal use/small fleets, along with “SSSD”.
Canonical built ADsys specifically to handle Active Directory GPOs, domain user privileges and Polkit rules automatically out of the box so you don’t have to fiddle with custom configuration files.
Good luck with your setup, and glad you are sticking with Ubuntu!
 . Anyway it seems gnomes sudo prompt is always promting localadmin rather then the logged in user that has sudo privileges. Stopping the prompts and being able to shut down the system would be enough. Software updates can be done from the terminal when needed.