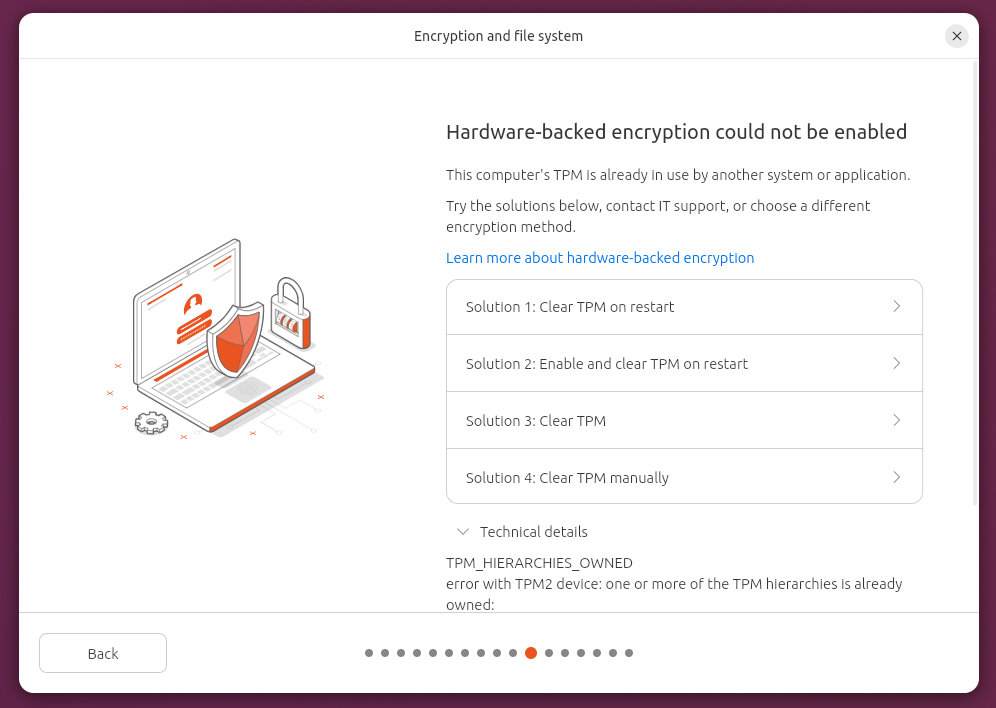
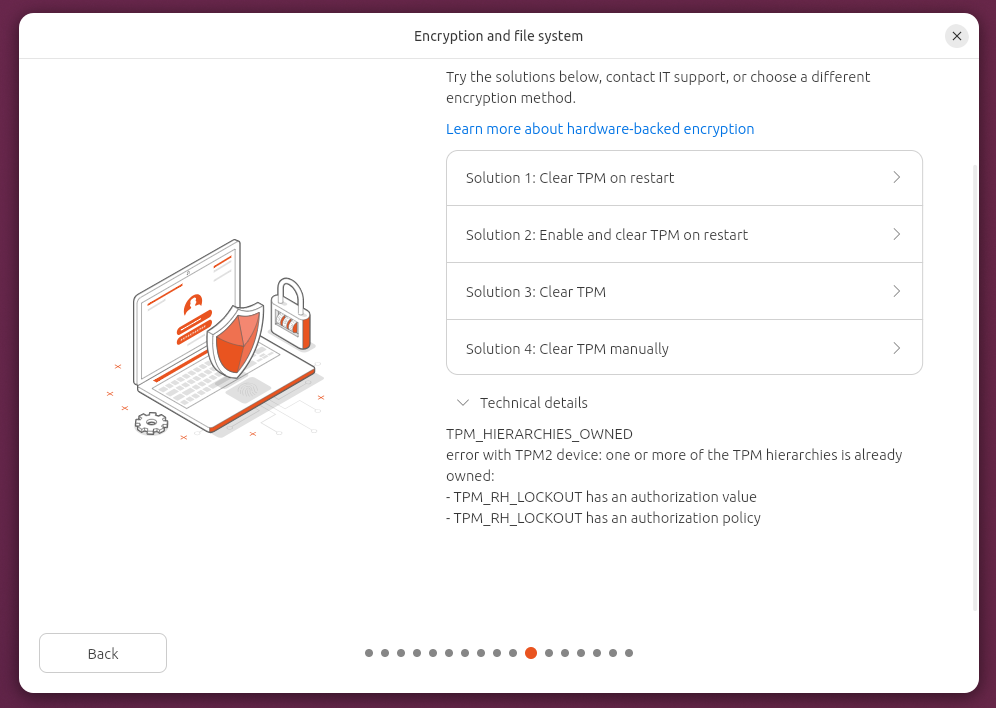
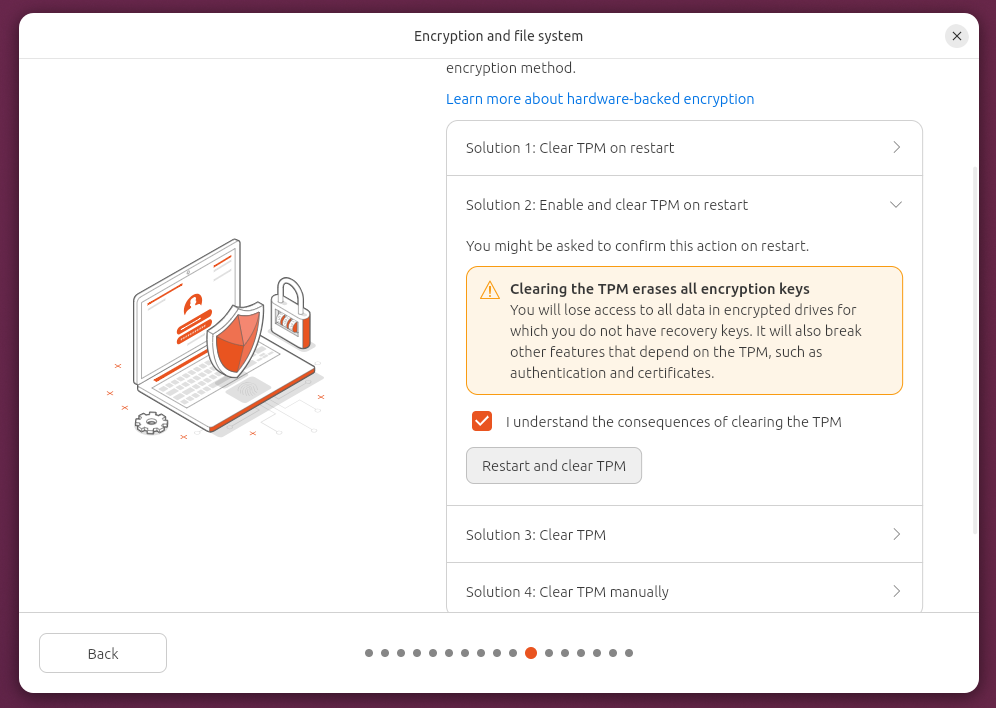
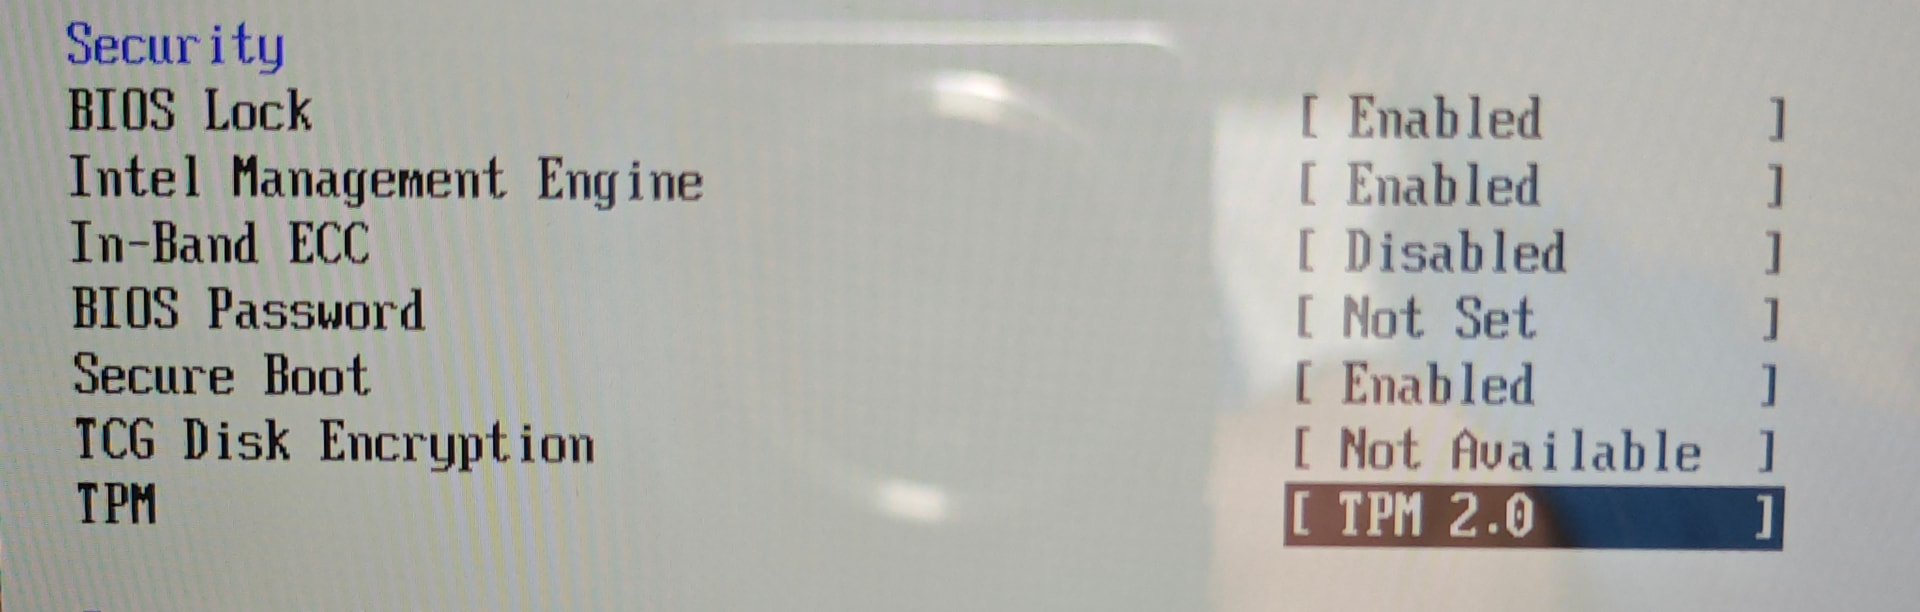
Sorry, I disable “secure boot” and TPM on all my devices.
They all work fine.
Sorry, I disable “secure boot” and TPM on all my devices.
They all work fine.
No, that option was, unfortunately, not offered.
Maybe this was because I used a custom install/partitioning? (I did check for an encryption option there, but did not see anything)
Hi. Just wanted to know if there’s something I can do to ignore the BootGuard requisite when installing Ubuntu 26.04 with hardware FDE. Thank you so much for your kind support here.
How is this matter progressing? Will the installer be updated before the first point release or is it certain that FDE requirements won’t be revised before then? (I mean, the BootGuard topic)
Thank you
Good morning. Were you able to lessen Boot Guard requirement for 26.04.1 release. Thank you so much for your attention.
Indeed, 26.04.1 will allow the end user to ignore the Boot Guard requirement. Documentation is at https://ubuntu.com/desktop/docs/en/latest/reference/hardware-backed-disk-encryption-requirements/
If your system does not have a hardware root of trust, the Ubuntu installer makes it mandatory to add a PIN or passphrase. After installation, you can disable the PIN or passphrase. However, your system won’t be protected against the described hardware and firmware threats.
That’s very good news! Thank you
Good evening,
So I tried installing Ubuntu with FDE. But I still couldn’t skip BootGuard.
I appreciate your attention.
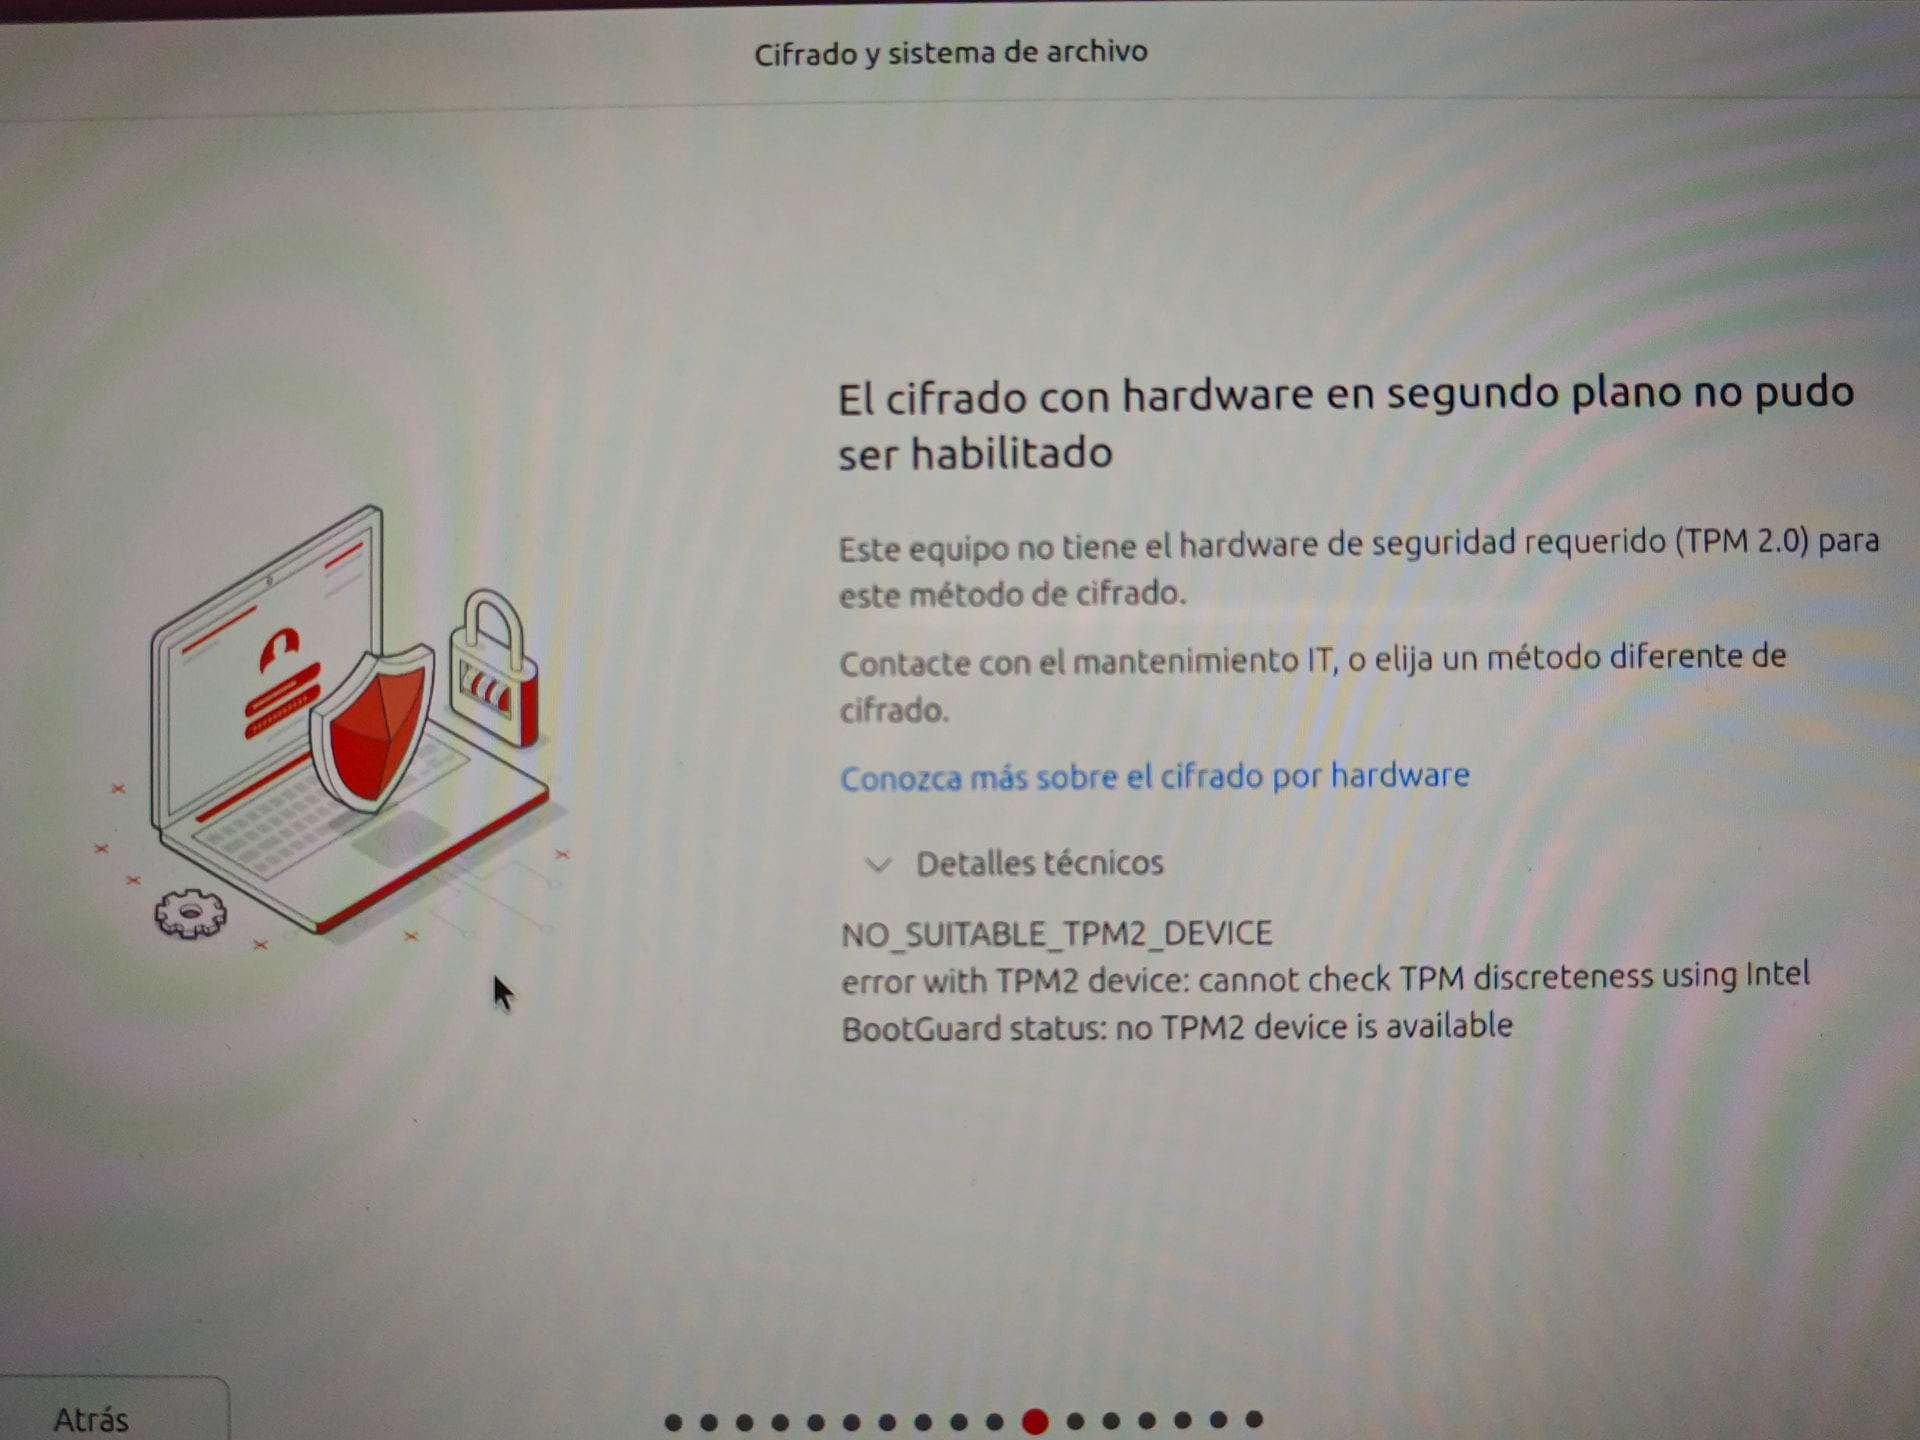
(Background hardware encryption could not be enabled.
This computer does not have the required security hardware (TPM 2.0) for this encryption method.
Contact IT support, or choose a different encryption method.)
It’s likely possible that the system you are using does NOT have a TPM that is modern which isn’t a BootGuard issue necessarily - it’s a hardware issue. What laptop or system are you using?
Thank you. This tablet: https://es.starlabs.systems/pages/starlite-specification.
I think it should work. Could be related to the Intel Media Engine?
So, the TPM on that device is an fTPM = a firmware TPM. It runswithin the firmware and processor as ‘software’ compared to a dedicated TPM chip.
From what I can tell, Ubuntu supports fTPM as well, but it needs to be explicitly enabled in the BIOS for the TPM features and functions in your computer. You’ll have to refer to the documentation for your system to go into the BIOS and enable full TPM functionality of the fTPM on your device in order for the TPM device to be revealed to the Ubuntu operating system at runtime.
Intel Media Engine has no impact on the fTPM/dTPM device components to my knowledge (and is disabled according to that spec page on your device)
Thank you. TPM 2.0 is turned on. There’s a ton of info about it on the BIOS page. May I send you a screenshot by DM?
Hi there. I contacted the manufacturer, providing the installer logs etc. It looks like that “the logs confirm that the TPM is available and correctly configured in the firmware. The failure is in Ubuntu’s hardware-backed-encryption eligibility check: it uses Intel’s BootGuard status to classify the TPM, and is incorrectly concluding that no TPM 2.0 device is available.
This is a known Ubuntu issue affecting a number of Intel systems with working TPMs. Canonical are tracking it here:
https://github.com/canonical/secboot/issues/455”
Hopefully it can be ironed out at some point. Let me know if there’s something I can do.
Kind regards and thank you so much for the support.